IBASE Cybersecurity and Product Security
Building Security into Every Stage of the Product Lifecycle

As industrial systems, edge computing platforms, and connected devices become increasingly integrated, product cybersecurity has become a fundamental requirement for maintaining stable and resilient operations. IBASE incorporates cybersecurity throughout the product lifecycle, including requirements definition, secure design, development, verification and testing, vulnerability management, security updates, and end-of-life planning. We continually refine our management framework in line with international cybersecurity standards and European Union regulatory requirements.

Cybersecurity Foundations and Management Framework

▌Management System Foundations

To continuously strengthen product cybersecurity management, IBASE is advancing the following priorities:

  • Continue planning product security functions and specifications in alignment with the IEC 62443 framework and CRA requirements, with phased implementation across product lines.
  • Enhance supplier cybersecurity assessments and expand the review and approval mechanisms for third-party components.
  • Adjust preparations for technical documentation and conformity assessment in step with the publication of EU harmonised standards.
  • Continue expanding the mechanisms for publishing security advisories and receiving vulnerability reports.

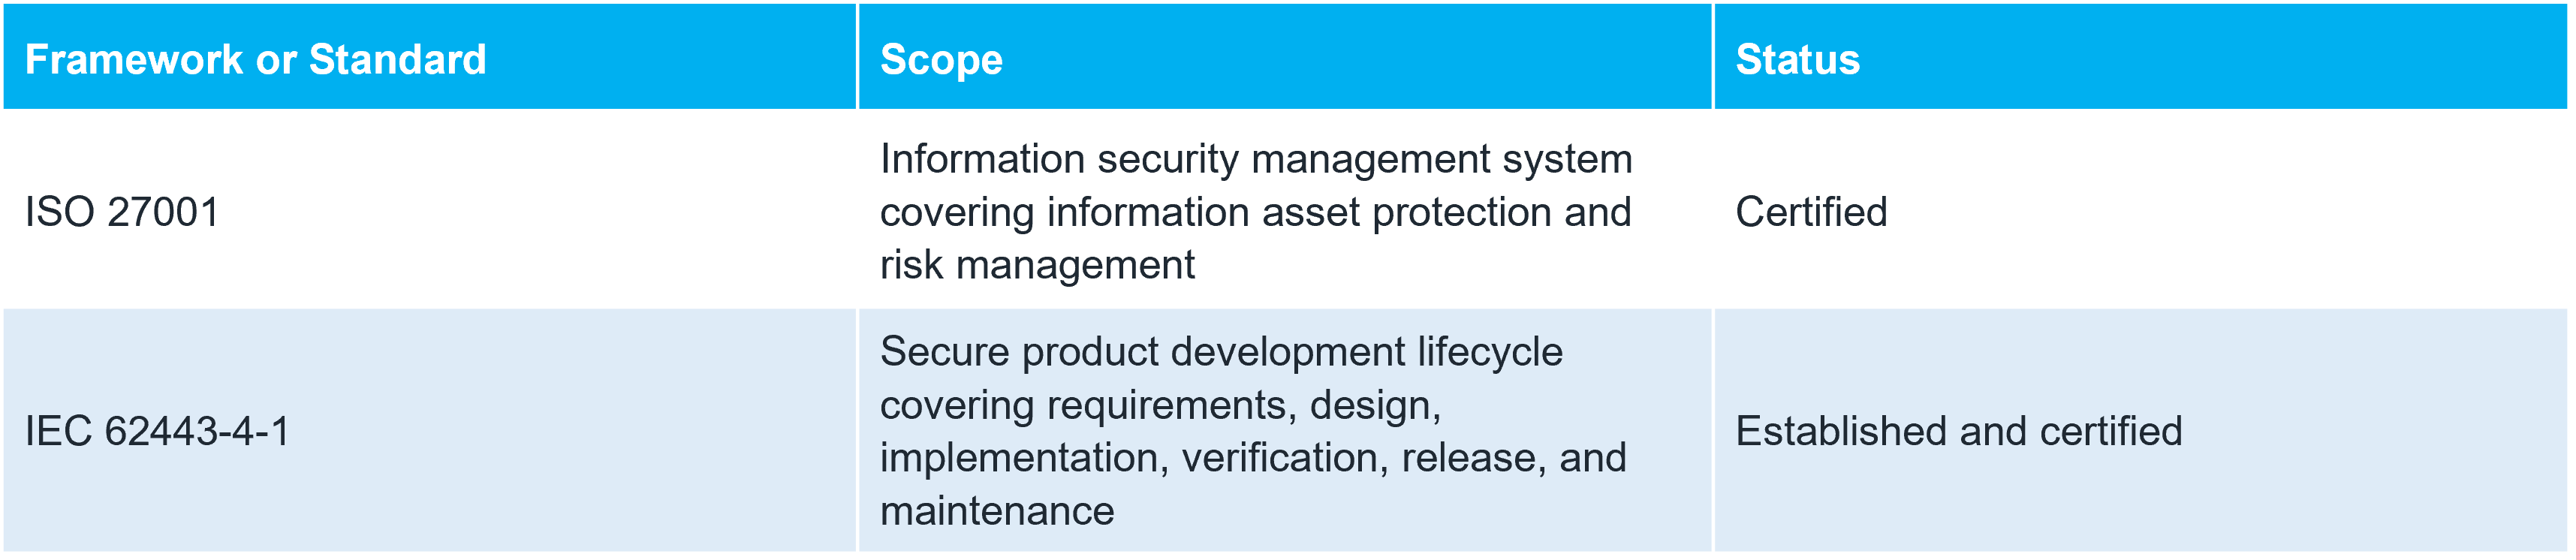
ISO 27001/IEC 62443-4-1

Certificates & Compliance Documents

European Union Cyber Resilience Act (CRA)

▌Overview

Products with digital elements made available on the European Union market are subject to the horizontal cybersecurity requirements of Regulation (EU) 2024/2847, the Cyber Resilience Act (CRA). The Act focuses on the following areas:

  • Security by design and secure by default: Manufacturers must identify and address cybersecurity risks during design and production. Products must be placed on the market with secure default configurations.
  • Supply chain management: Common requirements help reduce the risk that a single hardware or software vulnerability will cause a systemic cybersecurity incident. Manufacturers must manage known vulnerabilities and provide necessary security updates during the support period.
  • Disclosure obligations and market transparency: Manufacturers must provide security information and vulnerability reporting channels so users can make informed purchasing and usage decisions. They must also disclose the product's intended purpose, support period, and vulnerability reporting channel.

▌Implementation Timeline

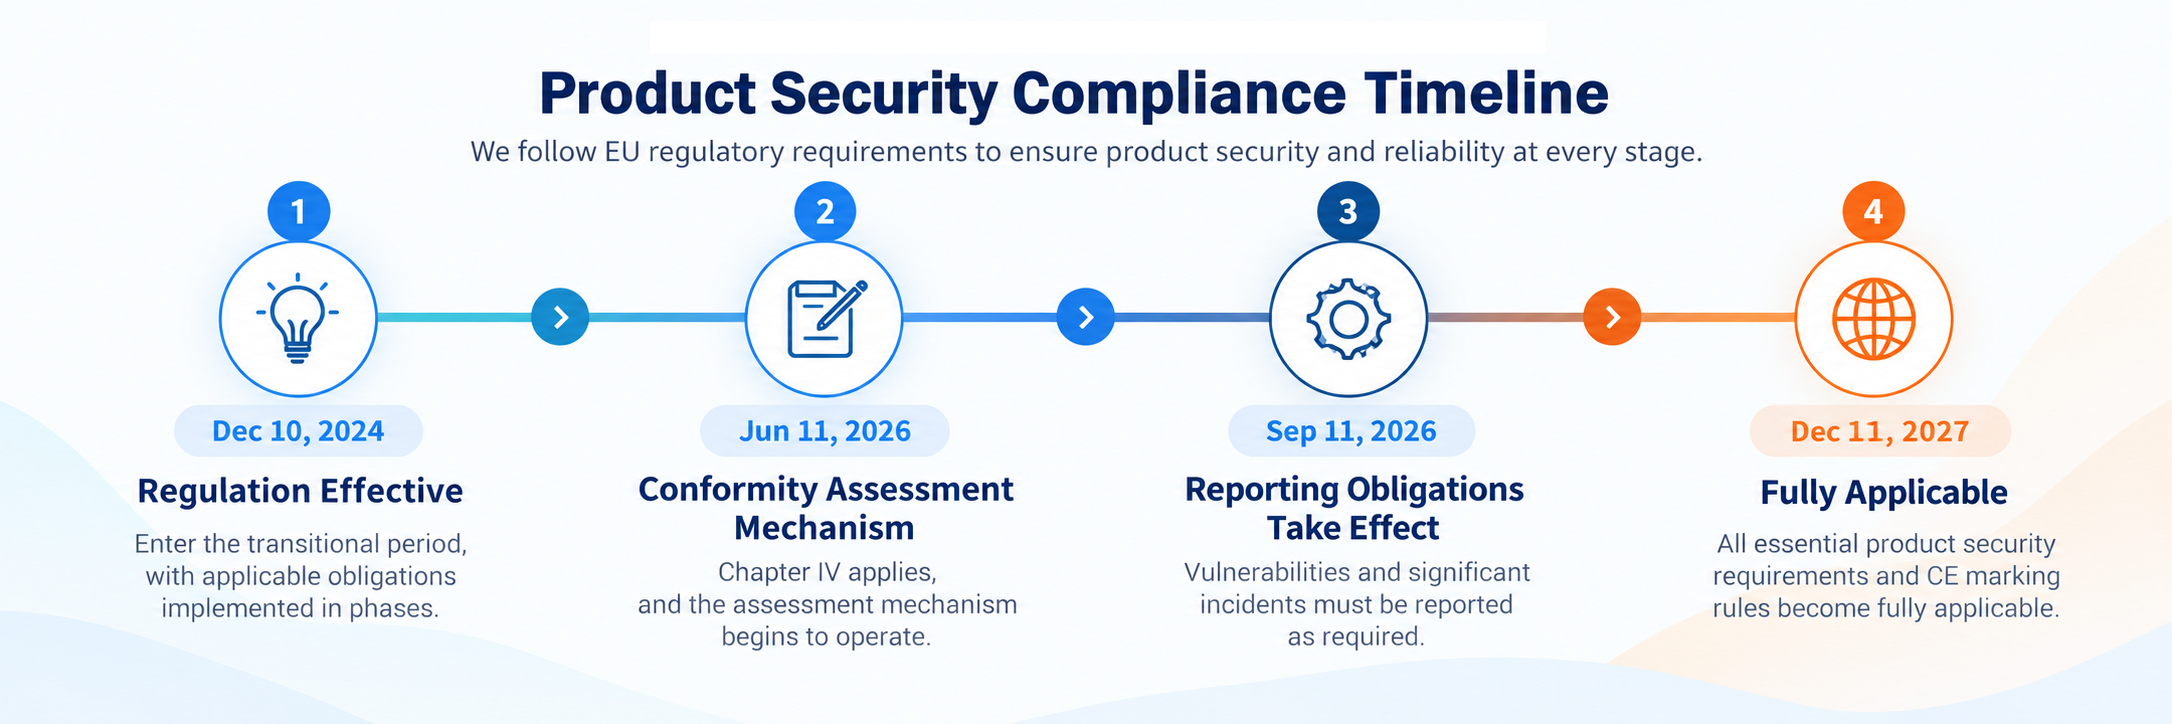
The CRA entered into force on 10 December 2024 and applies in phases:

On 27 July 2026, the European Commission published its first guidance on the application of the CRA. The guidance explains the interpretation of regulatory scope, substantial modification, support periods, reporting obligations, and risk assessment. It is a non-binding document and does not change the obligations or application timeline established by the regulation.

▌Reporting Obligations and Deadlines

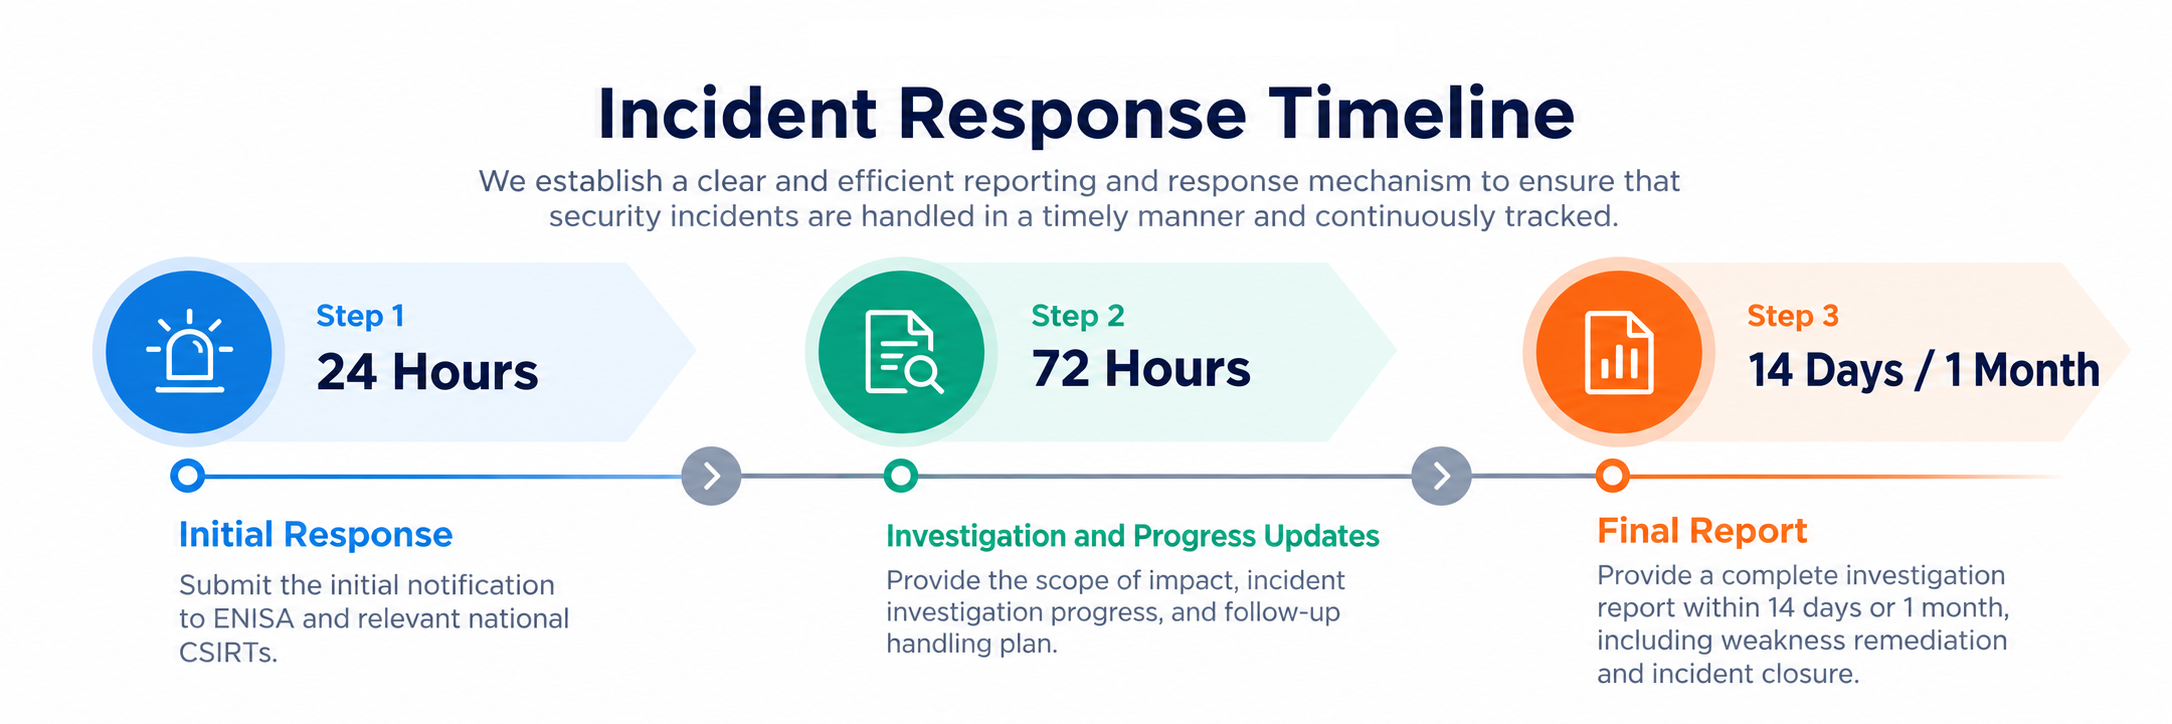
From 11 September 2026, manufacturers must report actively exploited vulnerabilities and severe incidents affecting product security through the prescribed channels. Reports are submitted through the EU reporting mechanism for distribution to ENISA and the relevant national CSIRT in accordance with the CRA. The reporting process follows three deadlines:

▌Product Classification and Conformity Assessment

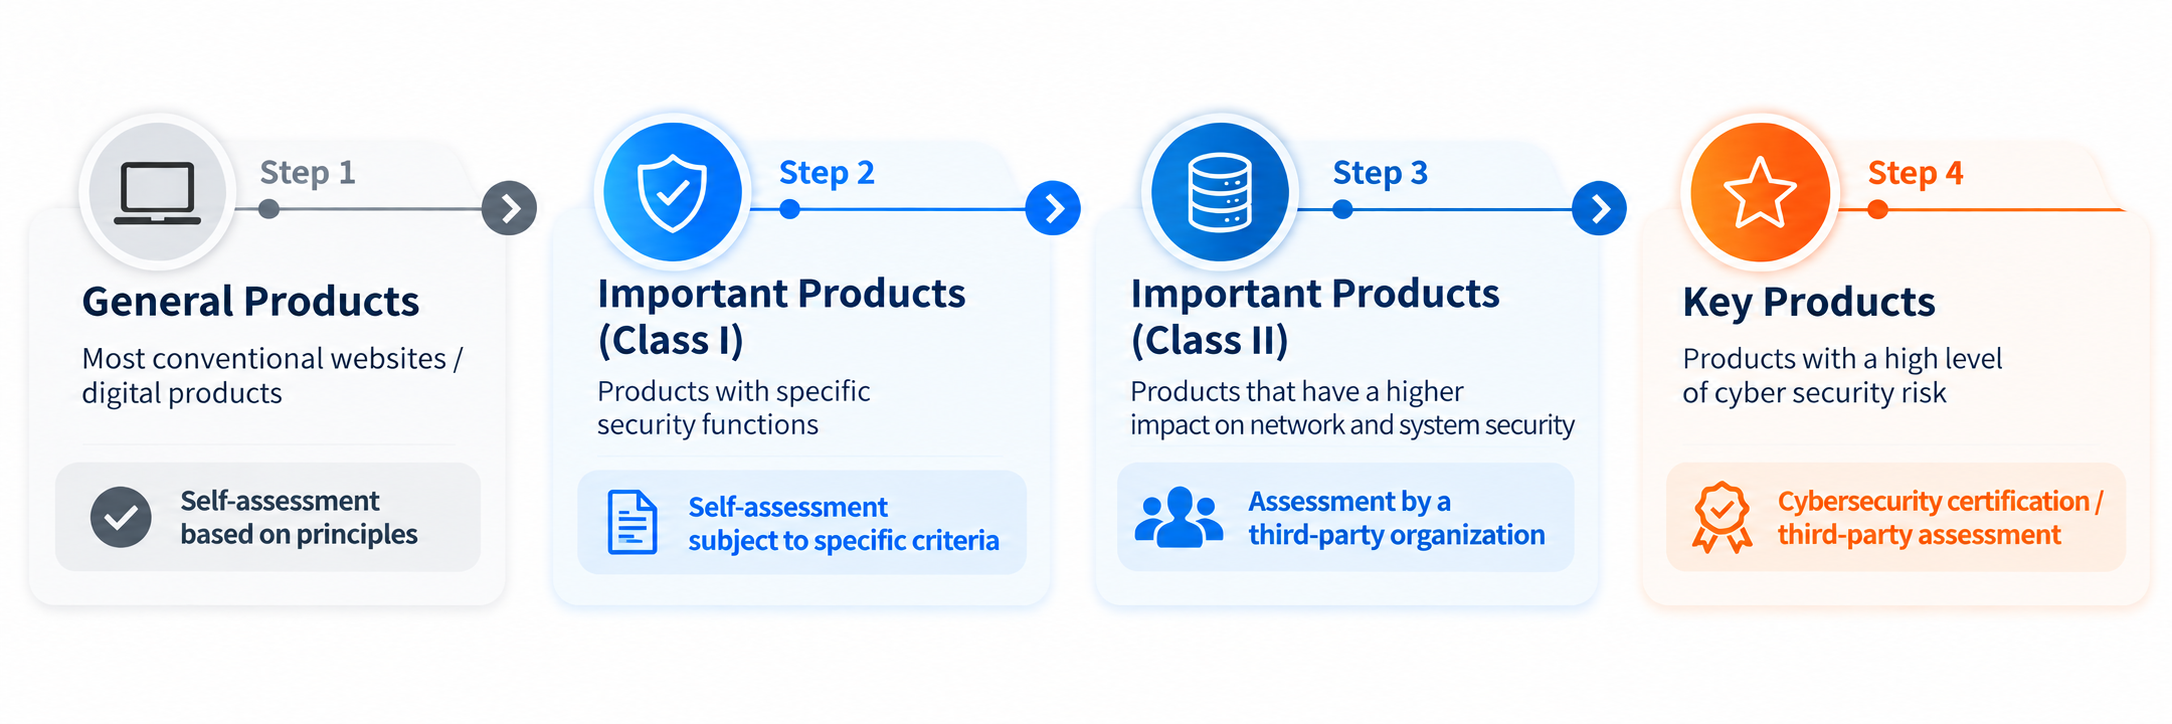
The CRA groups products according to cybersecurity risk. Classification determines the conformity assessment routes available for the product:

▌Roles in the Supply Chain

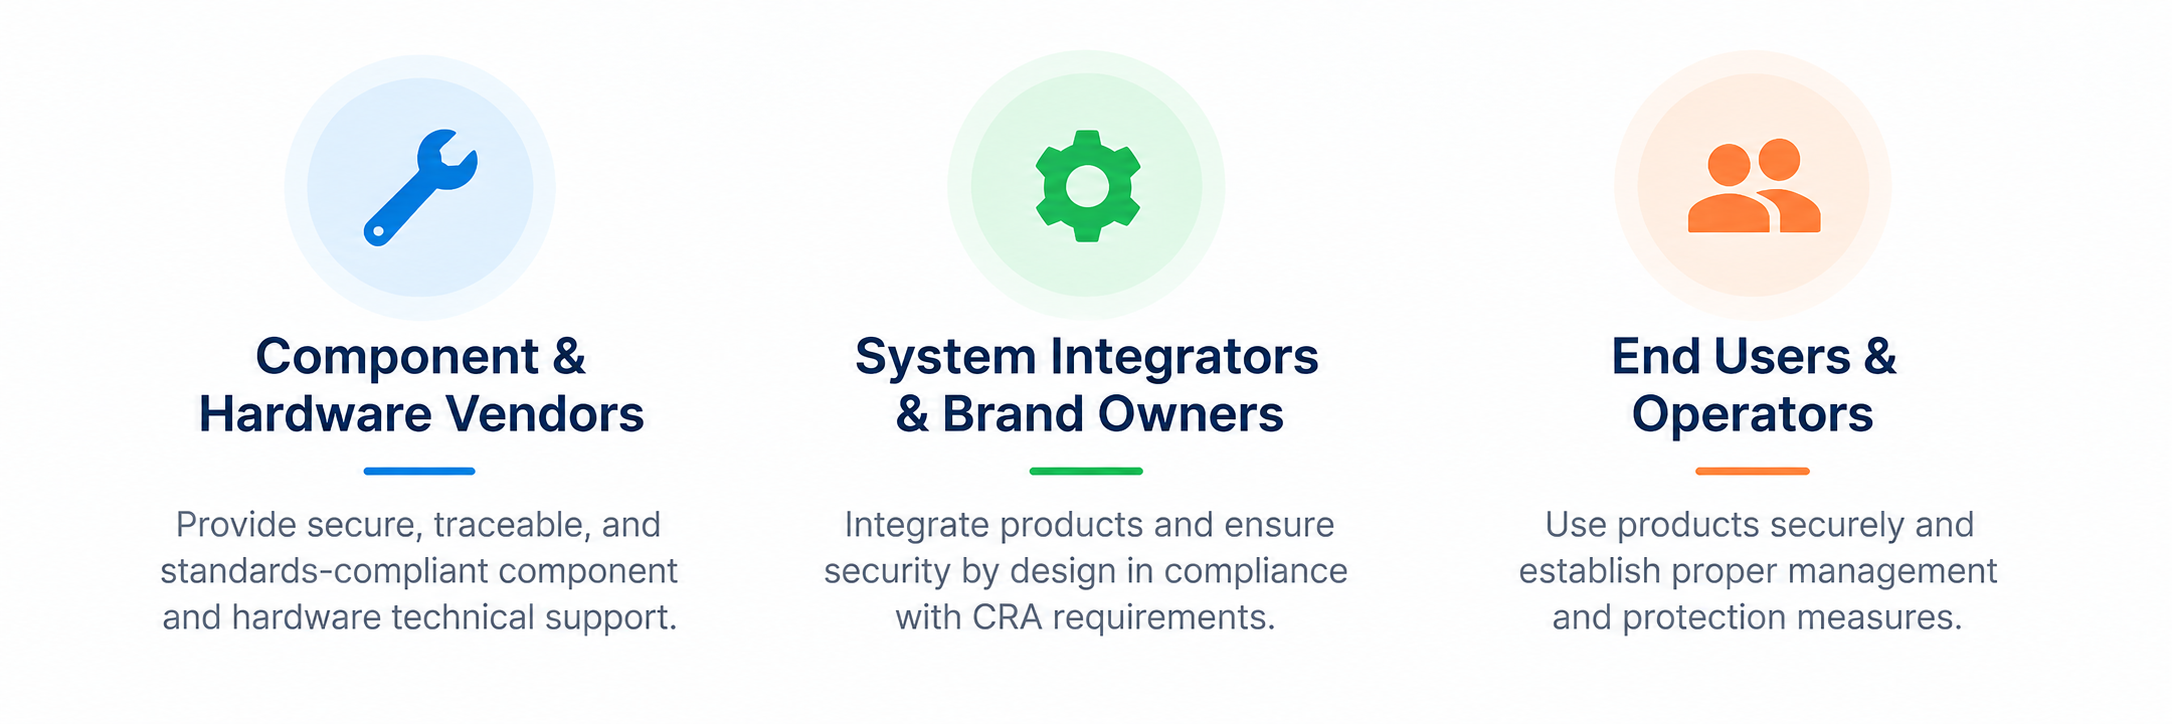
The CRA uses a shared-responsibility framework. A single product may involve several economic operators in the supply chain. Each party's role and obligations must be determined case by case based on the product form, delivery model, and the way the product is placed or made available on the market.

IBASE provides necessary technical information and security update support for the components and motherboards it supplies. We can also assist customers in discussing regulatory scope, product classification, and related documentation requirements. For product-specific discussions, contact your IBASE sales representative.

▌Key Manufacturer Obligations and IBASE's Approach

Key CRA ObligationIBASE Approach
  • Secure Design and Risk Assessment
  • Cybersecurity risk assessments must be conducted during the product design and production stages, and relevant records must be retained.
Conduct risk assessments and retain relevant records in accordance with the secure product development process.
  • Vulnerability Handling and Security Updates
  • Establish vulnerability handling procedures and provide security updates during the support period.
The PSIRT receives and handles vulnerability reports and releases updates according to the risk level.
  • Technical Documentation and Conformity Assessment
  • Prepare technical documentation and complete the conformity assessment required to obtain CE marking.
Prepare technical documentation according to the product category and adjust the preparation work based on the progress of standards development.
  • Incident and Vulnerability Reporting
  • Actively exploited vulnerabilities and major cybersecurity incidents must be reported within the prescribed time limits.
Establish reporting procedures and an external contact point in line with the September 2026 implementation timeline.
  • User Information Disclosure
  • Provide information such as the intended purpose, support period, and vulnerability reporting method.
Disclose support information and reporting channels in the product documentation and this dedicated section.


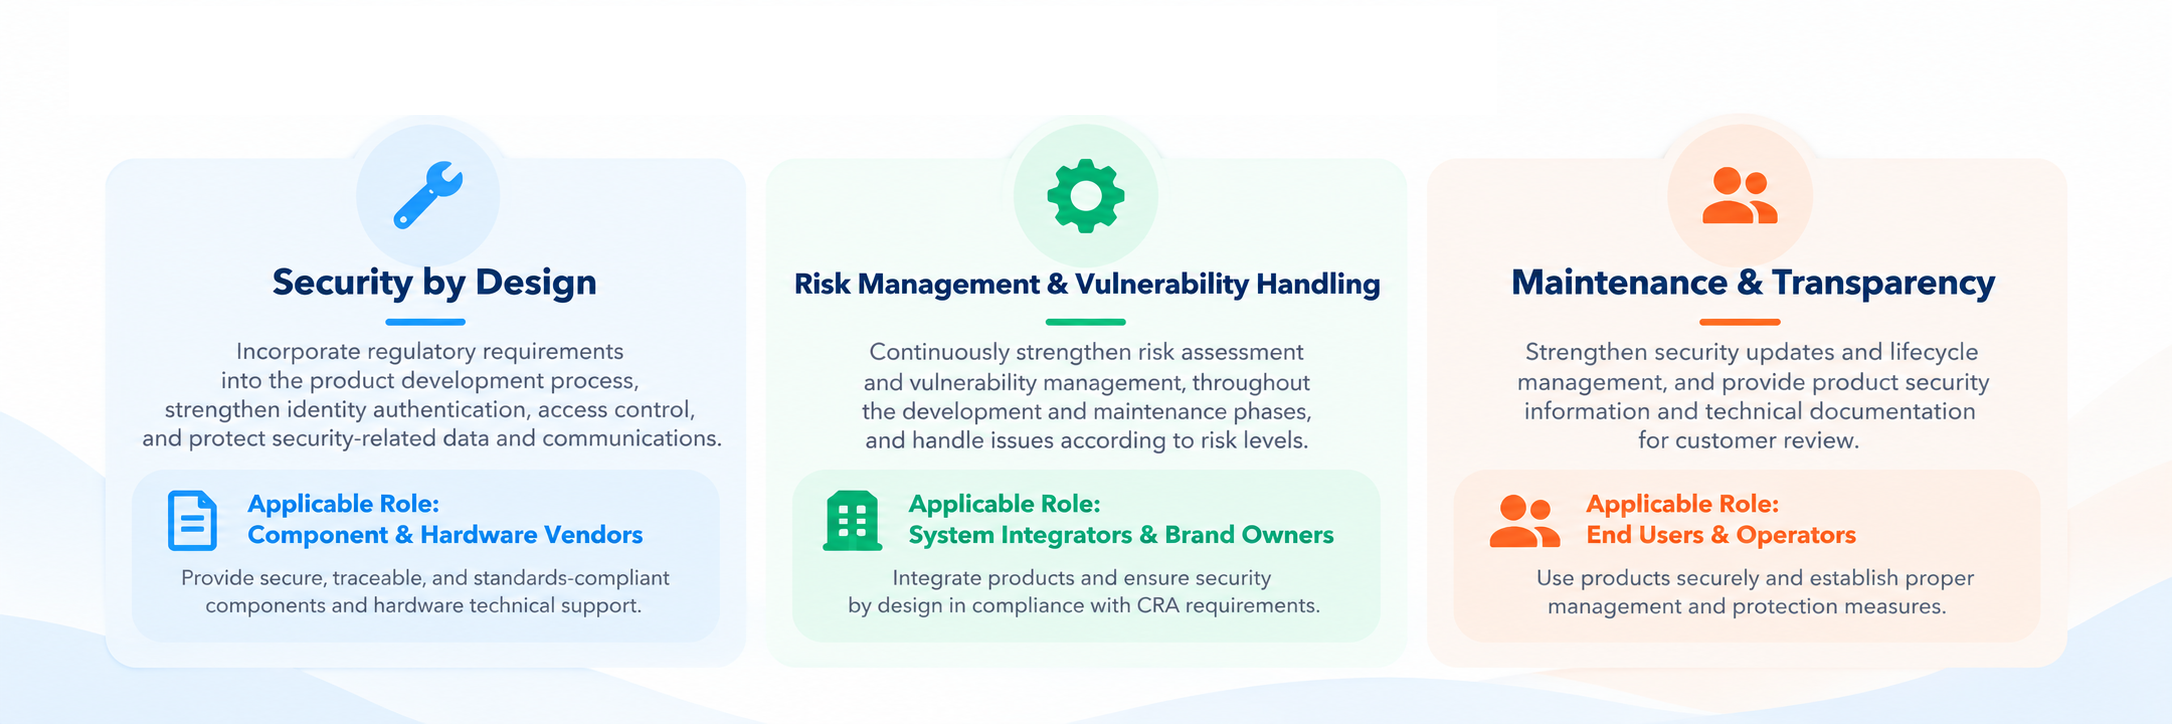
▌Product Cybersecurity Requirements

Each role has specific responsibilities to enhance product security and ensure regulatory compliance.

▌Relationship with Other Laws and Standards

Law or StandardPrimary Focus
CRA (EU) 2024/2847Products with digital elements themselves, covering obligations during design,placing on the market, and the support period
NIS2 (EU) 2022/2555Organizational and network security management for operators of critical infrastructure and essential services
RED (2014/53/EU), cybersecurity delegated regulation (EU) 2022/30, and EN 18031 seriesCybersecurity, personal data protection, and fraud prevention requirements for equipment with wireless communication functions
IEC 62443 seriesCybersecurity technical standards for industrial automation and control systems,including development process and product capability requirements


Vulnerability Reporting and Handling

The Product Security Incident Response Team (PSIRT) is the dedicated IBASE team responsible for receiving, assessing, and handling product cybersecurity vulnerability reports. When necessary, the PSIRT publishes security advisories and security updates and acknowledges receipt of a report. The handling method and completion schedule for each case depend on the severity of the vulnerability, the range of affected products, and the availability of feasible remediation measures.

▌How to Report a Vulnerability

If you discover a potential security vulnerability in IBASE Technology products, please email PSIRT@ibase.com.tw. To help us process and assess your report, please include relevant details in your email (such as the affected product model, firmware/software version, description of the vulnerability, and steps to reproduce it).

  • Contact information: Name, email address, region, country, and other relevant contact details.
  • Product information: Product model and version.
  • Vulnerability description: Technical details such as proof-of-concept code, attack method, and supporting documentation.
  • Potential impact: Possible attack scenarios and the scope of impact.


For security vulnerability reports and inquiries related to security advisories, please contact the Product Security Incident Response Team (PSIRT) at PSIRT@ibase.com.tw. For business matters such as requests for compliance documents, declarations, or component information, please contact our sales team using the details provided on the Contact Us page of the IBASE website. For product security updates and configuration issues, please contact our technical support team through the same webpage.


Completeness of submitted information: Please provide the product information currently known, a description of the issue, and any supporting evidence. PSIRT will record the report, conduct an initial assessment, and contact the reporter for additional information if needed.

Security Advisories

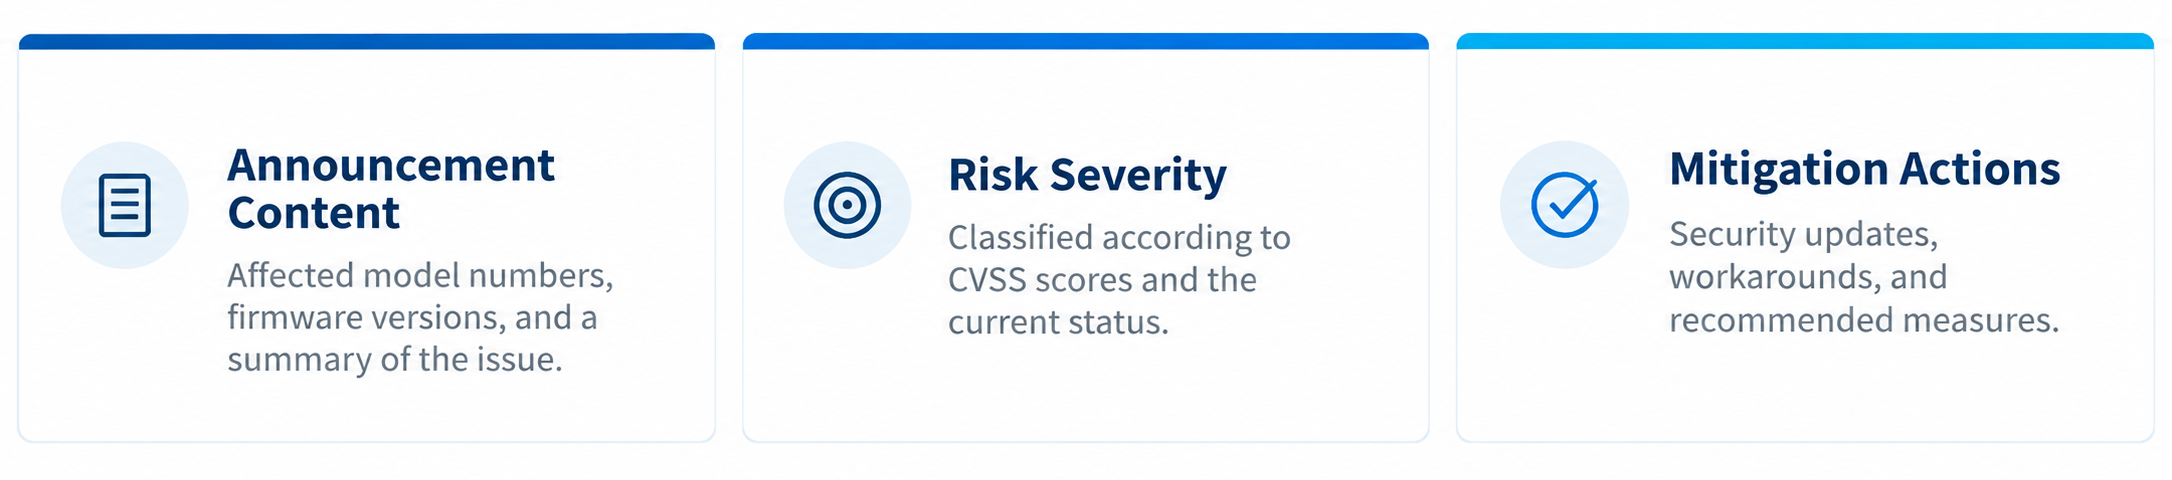
For confirmed cybersecurity vulnerabilities, IBASE will publish an advisory in this section and complete any required regulatory reporting. Each advisory may include:

Advisory ID Publication Date Affected Products Severity Status
                                                                                                                     No updates


Disclaimer: The information in this section is provided as is. IBASE determines the handling method and completion schedule based on vulnerability severity, the range of affected products, and feasible remediation measures. Results may vary by case. Content may be revised at any time, and the latest version published on this website prevails. 

For actively exploited vulnerabilities or severe incidents having an impact on the security of the product, IBASE will inform affected users in accordance with applicable regulations and provide information on any necessary risk mitigation or corrective measures.

Frequently Asked Questions

▌Q: What products and activities does the CRA cover?

A: The CRA is Regulation (EU) 2024/2847. It applies to products with digital elements, meaning hardware and software products that can connect directly or indirectly to other devices or networks. Products of this kind that are sold on the EU market, or otherwise made available in the course of a commercial activity, are in principle subject to the CRA. Whether the CRA actually applies depends on the product's intended purpose, its reasonably foreseeable use, and the exclusions specified in the regulation.

▌Q: Which IBASE products may fall within its scope?

A: The assessment depends on whether a product has direct or indirect data connectivity and whether it is made available on the EU market. Unless covered by other sector-specific legislation, many IBASE industrial computers, embedded systems, and related software products may be within scope. Applicability to a specific model must be determined based on its functional configuration, delivery form, and sales region. Contact your IBASE sales representative to discuss a specific model.

▌Q: How are products classified, and what does classification affect?

A: The CRA divides products into the default category, important products Class I, important products Class II, and critical products. Important and critical products are listed in Annexes III and IV. Classification determines the available conformity assessment route; higher-risk classes generally require greater third-party involvement.

▌Q: What are harmonised standards, and what is their current status?

CEN, CENELEC, and ETSI develop harmonised standards in response to the European Commission's standardisation request. These standards translate the CRA's essential requirements into verifiable technical specifications. CRA-related horizontal and product-specific standards remain under development and review, and their publication status should be checked against the latest EU notices.

▌Q: When do the reporting obligations begin, and what are the deadlines?

A: Starting September 11, 2026, manufacturers shall submit an early warning notification within 24 hours and a notification within 72 hours of becoming aware of an actively exploited vulnerability or a severe incident having an impact on the security of the product. A final report on a vulnerability shall be submitted no later than 14 days after a corrective or mitigating measure is available; a final report on a severe incident shall be submitted within one month after the incident notification.

▌Q: Does the CRA apply to products already on the market?

A: Starting September 11, 2026, the reporting and user notification obligations under CRA Article 14 apply, including to products that were placed on the EU market before that date. Other CRA requirements depend on the date each individual unit is first placed on the EU market, not on when the model was launched: Units placed on the market before December 11, 2027: In principle, only the Article 14 obligations above apply. However, if such units undergo a substantial modification on or after December 11, 2027, they must comply with the other applicable CRA requirements. Units first placed on the market on or after December 11, 2027: They must comply with all applicable CRA requirements, including product security, vulnerability handling, and conformity assessment. This applies even if the model has long been on the market.

▌Q: What may constitute a substantial modification?

A: A modification may be substantial when it changes a product's intended purpose or may affect its compliance with the essential cybersecurity requirements. Such a product may be treated as newly placed on the market. The nature and impact of the modification must be assessed case by case.

▌Q: What are the consequences of non-compliance with the CRA?

A: Authorities may require corrective action and may impose market measures such as withdrawal or sales restrictions. For infringements of essential cybersecurity requirements or key manufacturer obligations, administrative fines may reach EUR 15 million or 2.5% of total worldwide annual turnover for the preceding financial year, whichever is higher. Lower maximum fines apply to certain failures to provide information or cooperate with authorities.

▌Q: How do the CRA, NIS2, EN 18031, and IEC 62443 differ?

A: The CRA regulates the products themselves. NIS2 governs organizational management for operators of critical infrastructure and essential services. EN 18031 sets out requirements for equipment with wireless functions. IEC 62443 is a family of technical standards that can serve as a basis for establishing processes and product capabilities. The scope of each regulation and standard differs. In particular, the RED cybersecurity delegated regulation (EU) 2022/30 will be repealed as of December 11, 2027. From then on, the cybersecurity obligations of the relevant products shall be determined under the CRA, while the other applicable RED requirements must still be met.

▌Q: What is IBASE's role under the CRA?

A: Many IBASE products are components or motherboards intended for integration. The party that places the final product on the EU market under its own name or trademark is generally the manufacturer under the regulation and assumes the corresponding obligations. Roles depend on the actual transaction and market placement model. IBASE can assist customers in discussing their product architecture.

▌Q: What cybersecurity foundations and certifications does IBASE currently have?

A: IBASE is certified to ISO 27001 for its information security management system. It has also established a secure product development lifecycle in accordance with IEC 62443-4-1 and obtained certification. Implementation of relevant IEC 62443-4-2 requirements is being planned. Certificates are available in the Certificates and Compliance Documents section.

▌Q: Does IBASE provide an SBOM, and what happens if a supplier cannot provide one?

A: IBASE has established software bills of materials for its products and evaluates the method and scope of disclosure based on customer requirements and confidentiality conditions. IBASE generally requires suppliers to provide an SBOM for third-party components. If a complete SBOM cannot be provided, the supplier must provide alternative information sufficient for component identification, vulnerability analysis, and risk assessment. IBASE then assesses whether the component may be adopted.

▌Q: How can I report a cybersecurity vulnerability or request compliance documents?

A: Email cybersecurity vulnerability reports to PSIRT@ibase.com.tw and include the information listed in this section. For compliance documents, declarations, and component-related information, contact your IBASE sales representative.

About IBASE

Reliability

In house electrical, mechanical and thermal design with hardware/software reliability & compatibility validation.


Longevity

To ensure long-term supply, high-quality components are sourced with effective product lifecycle management.

Performance

Leverages the latest solutions from Tier 1 processor vendors to ensure high levels of computing performance.

Serviceability

Provides comprehensive after-sales services and technical support to ensure complete customer satisfaction.

February 2000

Founded

Taipei, Taiwan

Headquarters

TPEx 8050

Stock Code

By becoming an IBASE member, you can have access to the test reports, certifications, 2D/3D drawings and MTBF reports from our member site. Not a member? Join Now!